Know Your Customer: Turn Customer Risk Into a Clear Go Decision
See how AI-driven know your customer software scores risk and delivers a clear onboard, decline, or escalate call - not just raw data to sift through.
Quick Answer
A defensible KYC decision requires continuous evidence, clear risk weighting, and a documented recommendation to onboard, decline, or escalate. An AI agent can connect identity, ownership, sanctions, media, and behavioral signals into one review record, while keeping the underlying evidence available for analyst challenge and audit.
Introduction
Manual KYC review breaks down at the decision point: analysts receive documents, alerts, and search results, then must translate a fragmented file into a call they can defend. A Know Your Customer agent should reduce that interpretation burden, not simply generate more evidence. The practical shift is from a one-time onboarding file to continuous KYC monitoring that detects meaningful changes after the account is live. A useful recommendation must show which facts changed the risk posture and which unresolved facts still require human judgment.
Key Takeaways:
Risk decisions need linked evidence, not isolated screening alerts.
Ownership and sanctions checks require entity-level context.
Continuous monitoring turns material changes into reviewable decisions.
How Does Know Your Customer Software Produce a Defensible Decision?
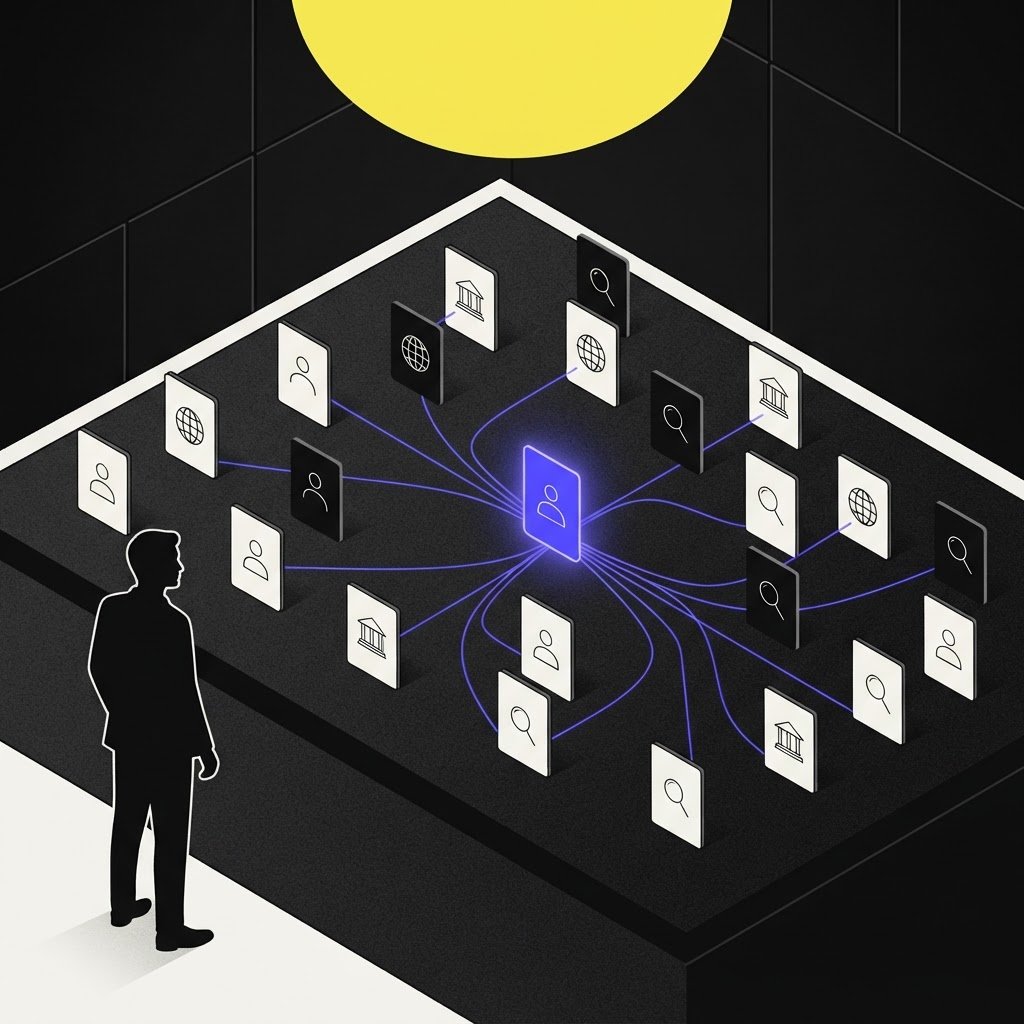
A strong KYC compliance workflow starts with a complete customer profile, then tests that profile against risk sources and converts the findings into a recommendation. The objective is not automatic approval at all costs. It is a consistent decision package that lets an analyst see what was verified, what was flagged, what was ruled out, and why the final disposition follows.
Build the customer record before scoring risk
The first pass should establish who the customer is, who controls the entity, and which details can be matched across records. A Know Your Customer agent can organize those checks into a repeatable investigation rather than leaving analysts to assemble a case from disconnected tabs.
Identity: Match names, addresses, dates, and official identifiers.
Entity status: Confirm legal existence and relevant registration details.
Ownership: Trace direct and indirect controlling parties.
Control: Identify the individual exercising managerial authority.
Evidence: Preserve sources beside each verified claim.
Map ownership as a risk pathway
Ownership is not a box to tick because risk can sit several layers above the customer entity. Under the beneficial ownership requirements, covered financial institutions must identify and verify people who own 25% or more of a legal entity and an individual who controls it.[1] That makes beneficial ownership mapping central to a decision record: the review needs to show the path from the legal entity to each relevant natural person.
How Do You Turn Screening Results Into a Risk Recommendation?
Screening creates signals, not conclusions. The operational value comes from resolving whether a signal belongs to the customer, ownership network, or an unrelated party with a similar name, then applying a documented policy to the result.
Resolve sanctions, watchlist, and media signals
An agent should compare match attributes, including identity details, geography, ownership relationships, and available source context before an alert reaches a disposition. Screening hit resolution is the process through which a possible match becomes a supported match, a supported non-match, or an escalation requiring analyst review.
Sanctions screening must also account for ownership, not just the customer name. OFAC’s 50 Percent Rule treats entities owned directly or indirectly in the aggregate by blocked persons at 50% or more as blocked.[2] A decision record should therefore state whether the ownership analysis creates exposure, rather than treating a clean entity-name result as the end of review.
Adverse media requires a different discipline because it can be relevant without proving misconduct. Adverse media monitoring should retain the publication, subject identity, date, allegation, and disposition rationale so that an analyst can distinguish a credible risk indicator from a weak or mismatched result.
Approach | Ownership tracing | Alert resolution | Ongoing monitoring |
|---|---|---|---|
Manual analyst review | Built case by case from registries | Analyst judgment per alert | Re-run manually on a schedule |
Point-in-time screening tool | One-time ownership snapshot | Raw match list, no disposition | Requires a new manual run |
Grep | Traces owners at 25% or more and the controlling individual, sourced per link | Resolves each hit to a disposition with a case note | Reopens the case only when a material change occurs |
The key tradeoff is simple: point-in-time screening closes an onboarding task, while ongoing screening of institutional customers preserves the ability to react when the customer’s risk profile changes.
Weight findings instead of counting alerts
Risk scoring should reflect the seriousness, reliability, and connection of each finding to the customer. A verified ownership link to a blocked party carries more weight than an unresolved name similarity, while a credible negative-news result may justify escalation rather than an automatic decline.
The Wolfsberg Group notes that negative news screening has no single universal approach. Its guidance describes conditional filtering using source attributes, including date-of-birth tolerance rules, which helps explain why policy-based matching logic matters more than raw alert volume.[3]
How Do You Run Continuous KYC Monitoring After Onboarding?
Customer risk is not static after approval. Changes in ownership, leadership, regulatory status, public reporting, or behavior can materially alter the original decision, which is why continuous monitoring should route only meaningful changes back into the review queue.
Define the events that reopen a case
Monitoring works when the team defines what constitutes a material change before alerts arrive. For example, a new beneficial owner, a sanctions-list update affecting a connected party, or newly relevant adverse media should reopen the prior file with the new evidence placed beside the original rationale.
Grep uses Loops and Monitors to run scheduled or event-triggered work and maintain an always-on screening surface for companies and counterparties. This helps enterprise KYC analysts scale because they can review a prioritized change record rather than repeat the full onboarding investigation each time.
Make the final call traceable
The final recommendation should be explicit: onboard when evidence is sufficient and risk is within policy, decline when a confirmed disqualifying condition exists, or escalate when material uncertainty remains. The record should capture the inputs reviewed, screening outcomes, risk factors, recommendation, reviewer action, and any policy exception.
That structure creates auditable compliance decision trails without pretending that every decision is fully automatic. Grep’s custom AI agents are designed for high-stakes work that needs traceable, citation-backed outputs, so the analyst receives a decision-ready brief rather than an unexplained score.
Conclusion
KYC teams scale when they standardize how evidence becomes a decision, not when they merely add more screening sources. Start with verified identity and ownership, resolve sanctions and media findings in context, weight the material signals, and use monitoring to reopen cases when risk changes. For banks and fintechs that need decision records that are defensible to compliance leadership, Grep helps turn ongoing checks into documented onboarding, decline, or escalation recommendations. The practical test is whether an analyst can explain the decision without reconstructing the investigation from scratch.
Ready to operationalize continuous KYC decisions? Try the Know Your Customer agent.
Frequently Asked Questions (FAQs)
What are the benefits of continuous KYC over one-time checks?
Continuous KYC provides ongoing visibility after onboarding by reopening the review when ownership, sanctions, media, leadership, regulatory, or behavioral signals change, whereas one-time checks preserve only the risk picture available at the moment of approval.
Can AI agents handle auditable institutional onboarding?
AI agents can support auditable institutional onboarding by collecting evidence, linking findings to sources, documenting screening dispositions, and producing a recommendation record that a human reviewer can challenge, approve, or escalate under the organization’s policy.
How can KYC operations scale without increasing headcount?
KYC operations can scale without increasing headcount when agents handle repeatable research, normalize evidence, resolve routine low-confidence alerts, and prioritize only material changes or unresolved cases for analyst review and accountable decision-making.
Can custom AI agents replace manual KYC analyst functions?
Custom AI agents should not replace accountable KYC analysts because analysts retain responsibility for policy interpretation and exceptions, but they can remove repetitive investigation work and make each analyst review more consistent and evidence-led.
What is the role of traceable AI in risk management?
Traceable AI in risk management connects each recommendation to the sources, checks, and reasoning used, enabling compliance teams to test the result, explain it to stakeholders, and preserve a record for internal oversight or regulatory review.
Sources
- Beneficial Ownership Information | FinCEN ↩
- 50 Percent Rule FAQs | OFAC ↩
- Negative News Screening FAQs | Wolfsberg Group ↩
About the Author