The Hidden Costs of Bad Vendor Data
When your vendor intelligence is incomplete, the costs compound in ways most teams never measure.
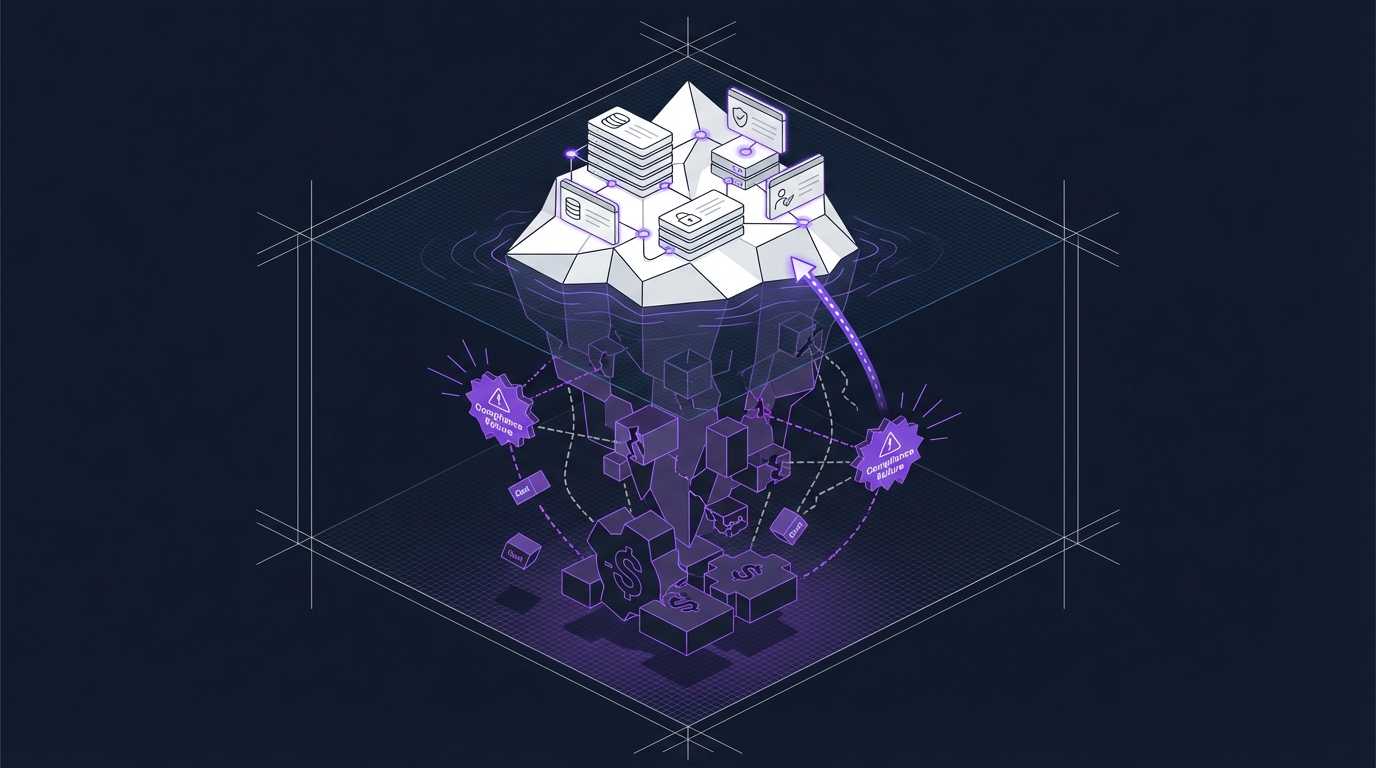
1The Data Quality Iceberg
Most organisations measure vendor risk by the number of assessments completed. Very few measure the quality of the data underpinning those assessments. This is a costly mistake.
Bad vendor data isn't obviously wrong — it's subtly incomplete. Your screening might catch a sanctioned entity by exact name match, but miss the beneficial owner operating through three shell companies. Your adverse media search might scan English-language sources but miss the fraud conviction reported in local press.
The costs of these gaps don't appear on a line item. They materialise as regulatory fines, reputational damage, and operational disruptions months or years later.
2Quantifying the Financial Impact
The financial consequences of inadequate vendor intelligence compound across multiple dimensions:
- Regulatory fines: AML/KYC violations average $2.2M per incident for mid-market firms. Major banks have paid billions.
- Remediation costs: Re-screening an existing vendor portfolio after a compliance failure costs 3-5x the original assessment.
- Business disruption: Vendor failures due to undiscovered risks cost an average of $1.5M in operational impact.
- Reputational damage: A single compliance failure linked to poor vendor screening can cost years of trust.
Compare these figures to the cost of comprehensive screening: approximately $50 per vendor with GREP AI. The ROI calculation is not subtle.
3The Five Most Dangerous Data Gaps
Our analysis of compliance failures reveals five recurring patterns of inadequate vendor intelligence:
- Beneficial ownership opacity: Screening the entity name without tracing the ownership chain to ultimate beneficial owners
- Jurisdictional blind spots: Checking domestic registries but missing foreign regulatory actions against the same entity
- Temporal gaps: Running a point-in-time check without historical adverse media analysis
- Network blindness: Assessing the vendor in isolation without mapping related parties and their risk profiles
- Source limitation: Relying on 2-3 databases when comprehensive coverage requires 50+
4Building a Data Quality Framework
Addressing vendor data quality requires a systematic approach:
- Define minimum source coverage: Establish which databases must be checked for each risk tier
- Automate the mechanical work: Use AI-powered research to ensure consistent, comprehensive coverage
- Require citations: Every finding should trace back to a verifiable primary source
- Monitor continuously: Point-in-time assessments are insufficient — risk profiles change
- Measure data quality: Track source coverage, finding consistency, and citation completeness alongside assessment volume
GREP AI addresses each of these requirements by default. Every report cites its sources, covers 50+ databases, and can be refreshed on demand for continuous monitoring.
Ready to Put This Into Practice?
Try Grep free and see how AI-powered research can transform your workflow.
Try GREP AI Free