Vendor Risk Assessment Software Pricing: What Buyers Pay in 2026
A 2026 breakdown of vendor risk assessment pricing models, typical costs by company size, and what separates cheap tools from defensible platforms.
Quick Answer
Vendor risk assessment software pricing is usually custom, because cost depends on vendor volume, monitoring scope, integration requirements, and audit expectations. In 2026, buyers should separate self-serve research plans from enterprise deployments, then budget for ongoing oversight rather than treating due diligence as a one-time project.
Introduction
Most pricing conversations fail because the quoted platform fee is only one part of the operating cost of vendor risk assessment. A lower-priced system can still create expensive work when analysts must chase evidence, reconcile screening results, and rebuild reporting for every review cycle. Banks, fintechs, and large enterprises need a model that accounts for criticality, regulatory scrutiny, and the growing requirement to observe third parties after onboarding. The real comparison is not software against software, but static questionnaires against an operating system for defensible decisions.
Key Takeaways:
Pricing rises with vendor volume, monitoring depth, integrations, and governance requirements.
Enterprise contracts should be evaluated against the labor required to sustain their controls.
Continuous monitoring changes both the subscription model and the evidence buyers need.
Vendor Risk Assessment Pricing Models
Pricing structures reveal how a platform expects work to be performed. Per-user licenses price access, per-assessment models price individual reviews, subscriptions bundle recurring activity, and custom enterprise agreements price a broader operating environment. Buyers should ask what happens when a vendor changes ownership, launches a new product, experiences a security event, or becomes critical to a regulated workflow.
How Common Pricing Structures Work
Every model can appear reasonable in procurement, but each shifts cost and operational risk differently. The useful question is whether the commercial structure matches the cadence of your vendor risk assessment software program rather than merely matching the initial onboarding project.
Per-seat licensing: Charges for named users who review, approve, or administer assessments.
Per-assessment pricing: Charges each time a vendor review or diligence package is initiated.
Tiered subscriptions: Bundles usage, data access, or workflow capacity into plan levels.
Enterprise contracts: Price shared access, security requirements, deployment, and support through custom terms.
Credit-based access: Charges for research runs or agent activity instead of user seats.
Why Published Prices Still Need Interpretation
Published pricing improves planning, but it does not automatically describe the full enterprise deployment. Grep publishes a free trial with 100 one-time credits. Its Pro and Ultra plans use different credit allocations, while team and enterprise deployments use custom terms. This makes the difference between self-serve evaluation and shared, governed implementation visible before a sales conversation.
In contrast, many third-party risk management platforms use custom pricing because the buyer's requirements may include SSO, VPC deployment, pooled usage, review workflows, data sources, integrations, and retention controls. A custom quote is not inherently a problem, but finance should insist on a clear definition of included activity, implementation work, renewal terms, and overage treatment.
What Drives Enterprise Vendor Risk Management Costs
Enterprise vendor risk management becomes more expensive when the program moves from collecting documents to making repeatable, reviewable decisions. The largest budget variables are not always visible on a rate card: evidence quality, risk-tiering logic, human approval steps, source coverage, and the burden of proving why an assessment reached its conclusion.
Continuous Monitoring Changes the Cost Base
Continuous monitoring adds recurring work because the platform must detect relevant changes and route them into a controlled review process. That cost can be justified when a relationship supports a critical activity, because Federal Reserve guidance emphasizes a banking organization's ability to provide adequate ongoing oversight and management of a third-party relationship.[1] The guidance emphasizes evaluating whether the banking organization can provide adequate ongoing oversight and management of the relationship.
Static screening produces a dated snapshot. Always-on monitoring creates a flow of signals, including website changes, leadership changes, job postings, and regulatory or compliance developments, but it only matters when teams can distinguish material changes from noise and preserve the reasoning behind escalation decisions. Monitoring design should accommodate changes in the relationship and preserve a controlled review process.
Capabilities That Increase a Quote
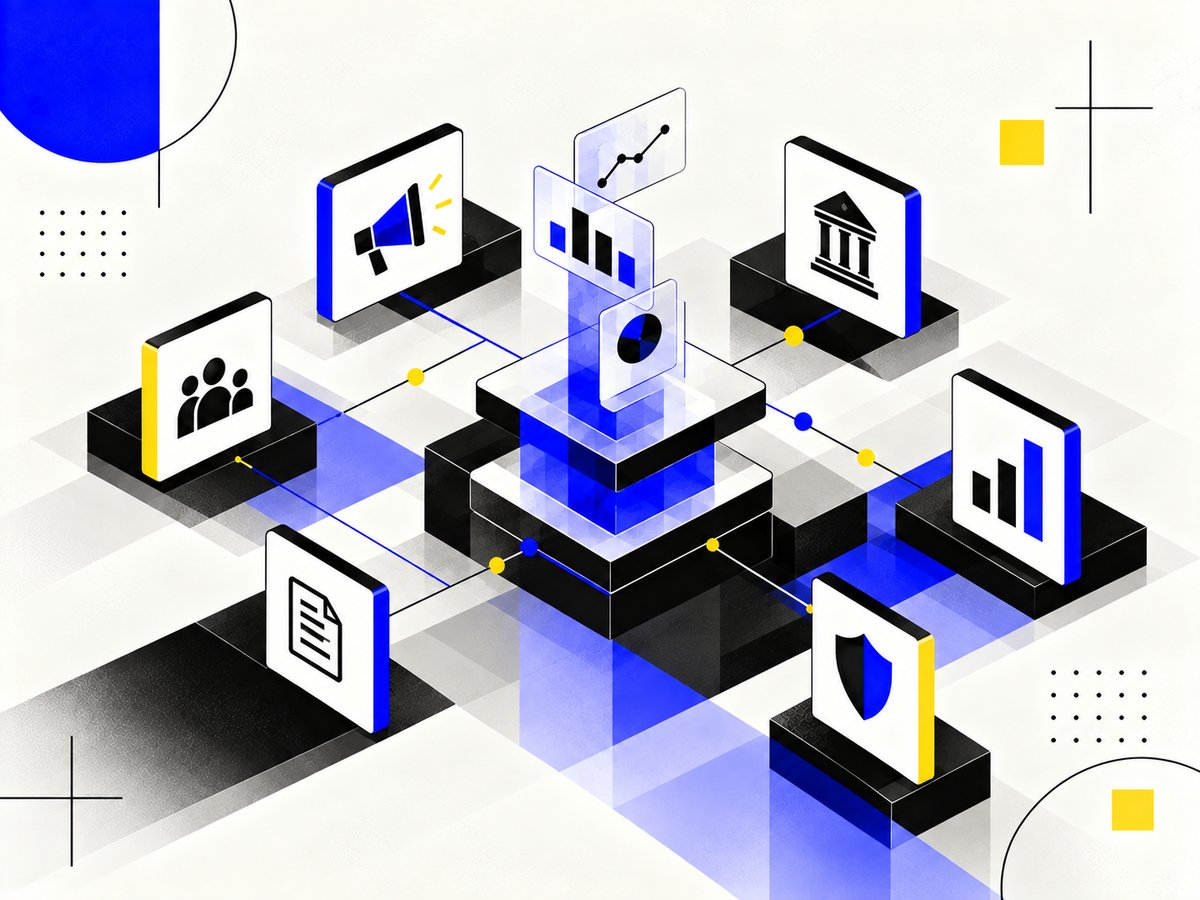
Costs rise when the system needs to work across compliance, procurement, legal, security, and business owners rather than serving one analyst group. That often includes third-party risk screening, integrated evidence capture, role-based controls, exportable reports, and audit trails that support vendor-risk reviews.
Additional cost usually follows the scope of integration and governance. SSO, VPC deployment, API access, shared agents, pooled usage, data retention policies, and formal approval records turn a research capability into part of the institution's control environment.
What to Budget for Vendor Risk by Company Size
There is no credible universal range for vendor-risk compliance costs at US financial institutions because vendors rarely publish comparable enterprise rates, and program scope varies sharply. Budgeting should begin with the operating model: how many relationships require review, which are critical, what evidence must be retained, and whether monitoring continues after approval.
Build a Budget Around Operating Requirements
Smaller teams can often start with a limited set of users or credits when the immediate goal is research and structured diligence. Larger organizations should model software, implementation, data access, internal review time, integration effort, and ongoing monitoring as separate budget lines, because a platform contract does not remove accountability for decisions. The same evaluation criteria carry over when assessing enterprise compliance software more broadly, not just vendor-risk-specific tools.
The table below compares the commercial models buyers will encounter. It does not present a market price range because public enterprise pricing is often undisclosed, and unsupported benchmarks would create false precision.
Pricing model | What determines cost | What buyers should confirm | Operational tradeoff |
|---|---|---|---|
Per-seat SaaS | Named users and plan tier | Reviewer access, permission levels, and seat changes | Can restrict participation across business owners |
Per-assessment | Reviews initiated or completed | Reassessments, renewals, and monitoring events | Spend can rise with program activity |
Credit-based AI access | Research runs and included credits | Credit validity, top-ups, data access, and API scope | Links spend to work performed |
Custom enterprise | Security, deployment, shared access, and support | Implementation, integrations, monitoring, and renewal terms | Supports broader governance requirements |
The practical takeaway is simple: compare the included unit of work, not just the annual contract figure. A lower subscription can be more expensive if it leaves teams performing manual evidence collection and repeat analysis outside the platform.
How Large Enterprises Should Evaluate an Enterprise Quote
For large enterprises, the meaningful question is whether the platform can manage vendor risk at scale without creating a parallel manual process. Grep's strongest traction today is among enterprises with roughly 5,000 to 10,000+ employees, where custom agents, shared access, and ongoing work across departments can matter more than a narrow questionnaire workflow.
Ask the vendor to demonstrate a real critical-vendor review from initial request through decision trail, then show what happens when new information changes the risk posture. This is also where vendor SOC 2 tracking should be evaluated as part of the full evidence record, not as an isolated document-chasing task.
How to Compare Quotes Beyond Sticker Price
A credible evaluation tests the cost of producing an auditable decision, not the cost of opening an account. The platform should show how it captures sources, identifies uncertainty, handles approvals, and creates a record that compliance, legal, internal audit, and the board can inspect.
Test the Workflow, Not the Demo Script
Use a high-stakes vendor scenario with conflicting sources, incomplete documentation, and a meaningful change after the initial review. Ask whether the platform can support vendor due diligence automation while preserving citations, reviewer judgment, and the evidence needed to defend the outcome.
For banking organizations, this scrutiny is not optional theater. The Federal Reserve guidance emphasizes evaluating whether the banking organization has adequate staffing, expertise, controls, and contingency plans to oversee the relationship on an ongoing basis. The guidance calls for evaluating the proposed third party's impacts and the organization's ability to oversee the relationship. Effective oversight may require capabilities and controls that can be adapted over time for the business arrangement. In practice, that means quote evaluation should test whether the platform can coordinate evidence and approvals across those disciplines rather than leaving each function with disconnected records. It should also show how external support can be incorporated without losing ownership, traceability, or a clear decision record.
Apply those principles directly in quote evaluation. For each relationship, document whether the program uses a relationship-level criticality or risk designation, or identifies the critical activity and the third party that supports it. Then map the required oversight to that decision: higher-risk and critical activities warrant more comprehensive and rigorous management, while a lower-risk relationship may require a proportionate workflow. Request an example that shows the underlying sources, the owner of each approval, the unresolved questions, and the process for revisiting the conclusion when a material change occurs. This avoids treating every vendor as interchangeable and gives procurement, compliance, risk, technology, and legal teams a shared basis for judging whether a platform supports the controls the relationship requires.
Price AI Agents as an Operating Capability
AI-agent-based platforms change the procurement conversation because the unit of value is not only a form, workflow, or report. A custom agent can conduct due diligence, compile traceable research, and produce deliverables, while Loops and Monitors run scheduled or event-triggered workflows and keep watch for material changes.
Grep frames this as custom AI agents for high-stakes work, with outputs designed to be traceable, auditable, and defensible to a board or regulator. Before committing, evaluate AI vendor risk management against the controls your team already needs: scoped credentials, retention rules, source-level evidence, human sign-off, and an exportable decision trail.
Regulatory expectations are still evolving. The FDIC's proposed interagency third-party risk management guidance allowed 60 days for comments after its September 2026 publication in the Federal Register, with the comment period closing in November 2026.[2] The related Federal Register notice for the proposed guidance provides another authoritative reference point, a reminder that program design should remain adaptable rather than hard-coded around a single assessment template.[3] Buyers should therefore assess whether workflows, evidence requirements, risk classifications, and approval paths can be revised without forcing a wholesale replacement of the operating model.
Grep Versus Microsoft Copilot for Vendor Risk Assessment
Vendor risk and compliance teams often already have Microsoft Copilot available through an existing Microsoft 365 license, which raises the question of whether a dedicated platform is needed at all. The honest comparison is about what each tool is built to produce.
Evaluation dimension | Microsoft Copilot | Grep |
|---|---|---|
Primary design intent | General productivity assistant across Microsoft 365 apps | Custom agents built for vendor risk and due diligence research |
Evidence trail | Conversation history, not a structured citation record | Claim-level citations tied to source documents |
Monitoring for new risk signals | Not a built-in capability | Scheduled or event-triggered monitoring of vendor changes |
Reviewer sign-off | No native approval workflow | Exportable decision trails for audit and sign-off |
Conclusion
Vendor risk assessment software should be budgeted as a recurring control capability, not as a one-time procurement expense. Compare quotes against the volume of reviews, the depth of monitoring, governance requirements, and the analyst effort left outside the product. For enterprises that need due diligence and continuous oversight with evidence that can withstand scrutiny, Grep is the choice when its custom agents, Loops and Monitors, and audit-ready outputs match the program's operating model. A transparent rate card is useful, but the durable decision comes from testing the full path from signal to defensible action.
Need a clearer view of ongoing diligence costs? Explore Grep's Pricing for transparent access options.
Frequently Asked Questions (FAQs)
How to automate vendor risk assessments for enterprises?
Automating vendor risk assessments for enterprises means using structured agents and workflows to gather evidence, apply risk logic, route exceptions for review, and retain source-backed decision records, while designated owners remain accountable for material judgments and approvals.
What are the benefits of continuous vendor monitoring over one-time checks?
Continuous vendor monitoring identifies material changes after onboarding, such as leadership, regulatory, website, or compliance signals, so teams can reassess exposure when it changes rather than relying on a diligence package that becomes stale.
How do custom AI agents support audit-ready compliance?
Custom AI agents support audit-ready compliance by producing traceable research outputs with citations and preserving the reasoning, source material, review steps, and approvals needed for an internal audit, regulator, or board-level challenge.
What is the difference between vendor risk tools and AI agents?
Vendor risk tools commonly organize questionnaires, workflows, and records, while AI agents can perform defined knowledge work such as research and due diligence, provided their outputs remain governed through evidence, permissions, and human review.
What does vendor risk assessment software cost for US financial institutions?
The cost of vendor risk assessment software for US financial institutions varies by vendor count, criticality, monitoring requirements, integrations, security controls, and deployment model, so buyers should obtain a scoped quote instead of relying on generic market averages.
Sources
- Interagency Guidance on Third-Party Relationships (federalreserve.gov) ↩
- Proposed Interagency Third-Party Risk Management Guidance and Issuance of Joint Statement on Community Banks' Engagement with Core Service Providers | FDIC.gov (fdic.gov) ↩
- Federal Register notice (federalregister.gov) ↩
About the Author